
Extend AWS application security
Go beyond basic cloud-native protections by adding advanced threat detection, bot mitigation, and API security—without changing how your AWS applications are built or delivered.


Fully managed SaaS WAF, API Security, and Bot Protection. Deploy across AWS and hybrid environments in minutes. Zero architecture changes. Minimal operational overhead.

Stop advanced attacks, including bots and automated threats, before they impact your applications and APIs.

Stay within AWS. No traffic detours, no disruption. Just seamless protection alongside services like CloudFront.

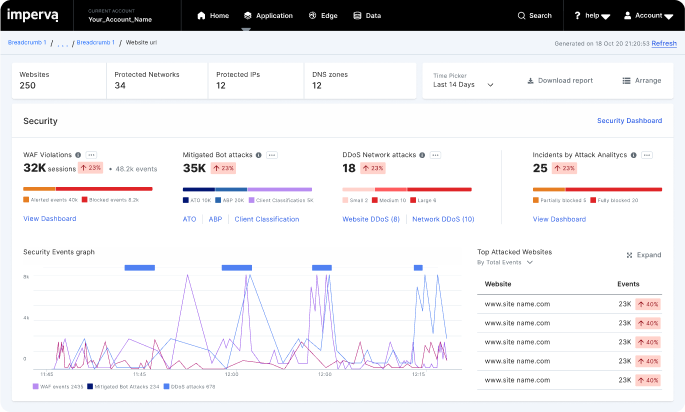
See what’s happening and act faster with unified policies and a single view of application risk.
Read the report to see why Imperva was named a Leader in KuppingerCole’s Leadership Compass 2025 for Web Application and API Protection (WAAP)—and how our platform protects your applications and APIs at scale, with confidence.
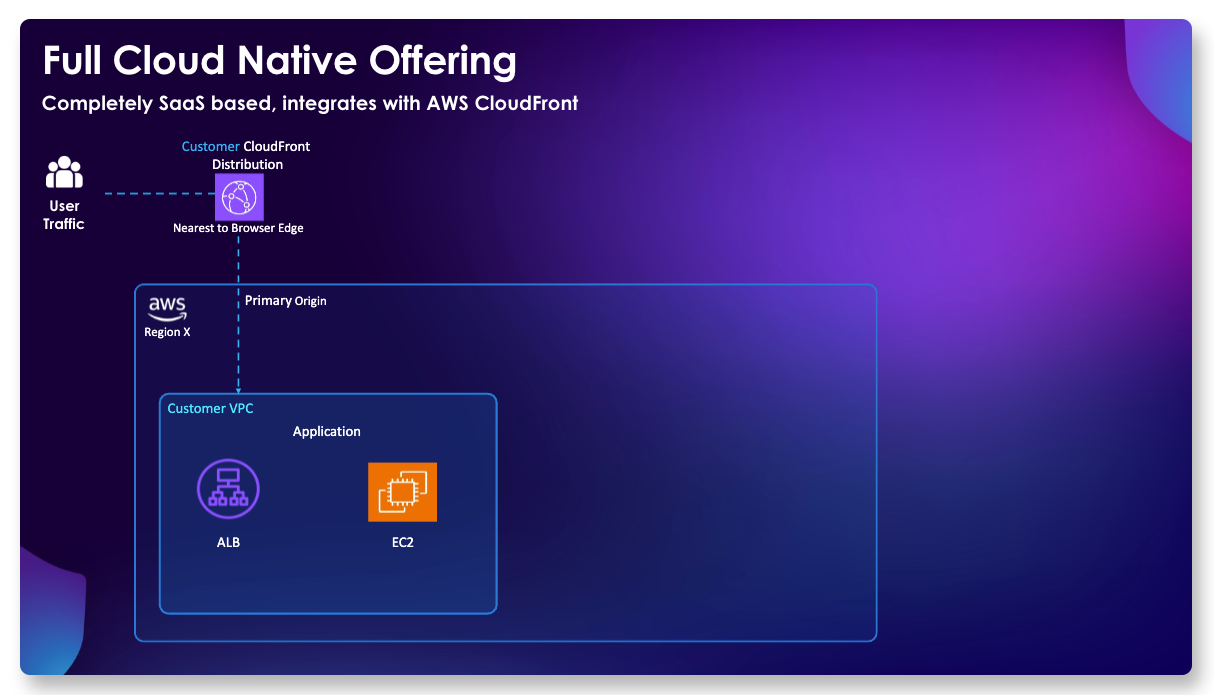
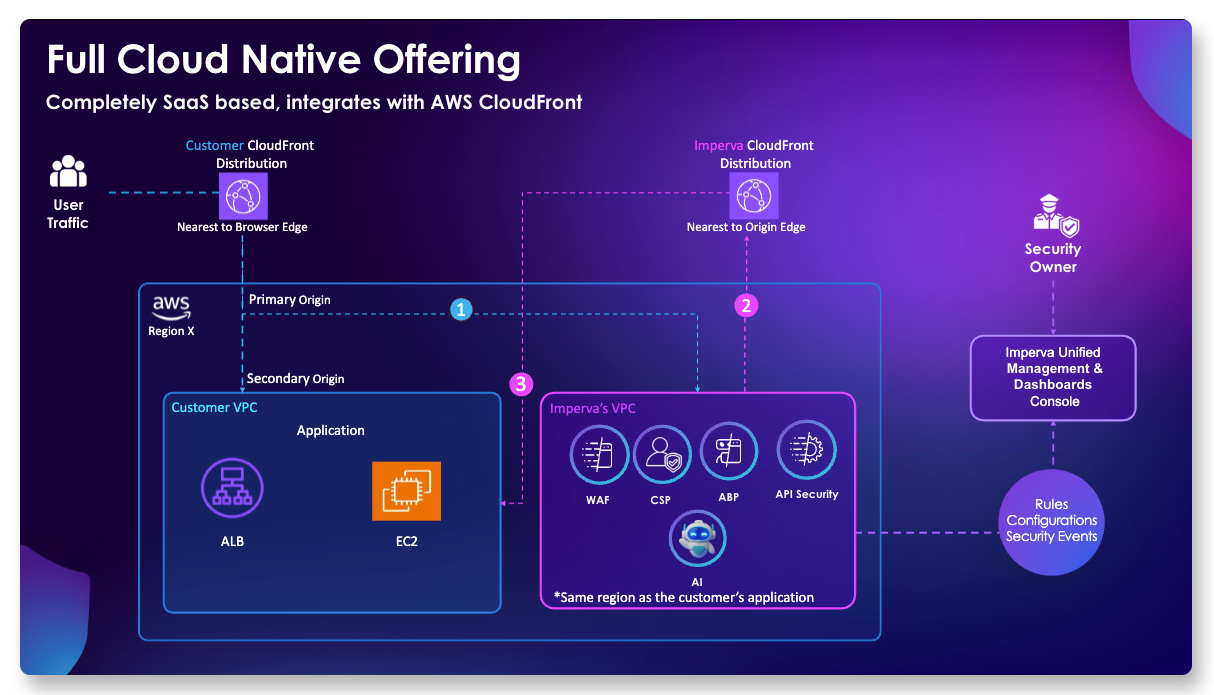
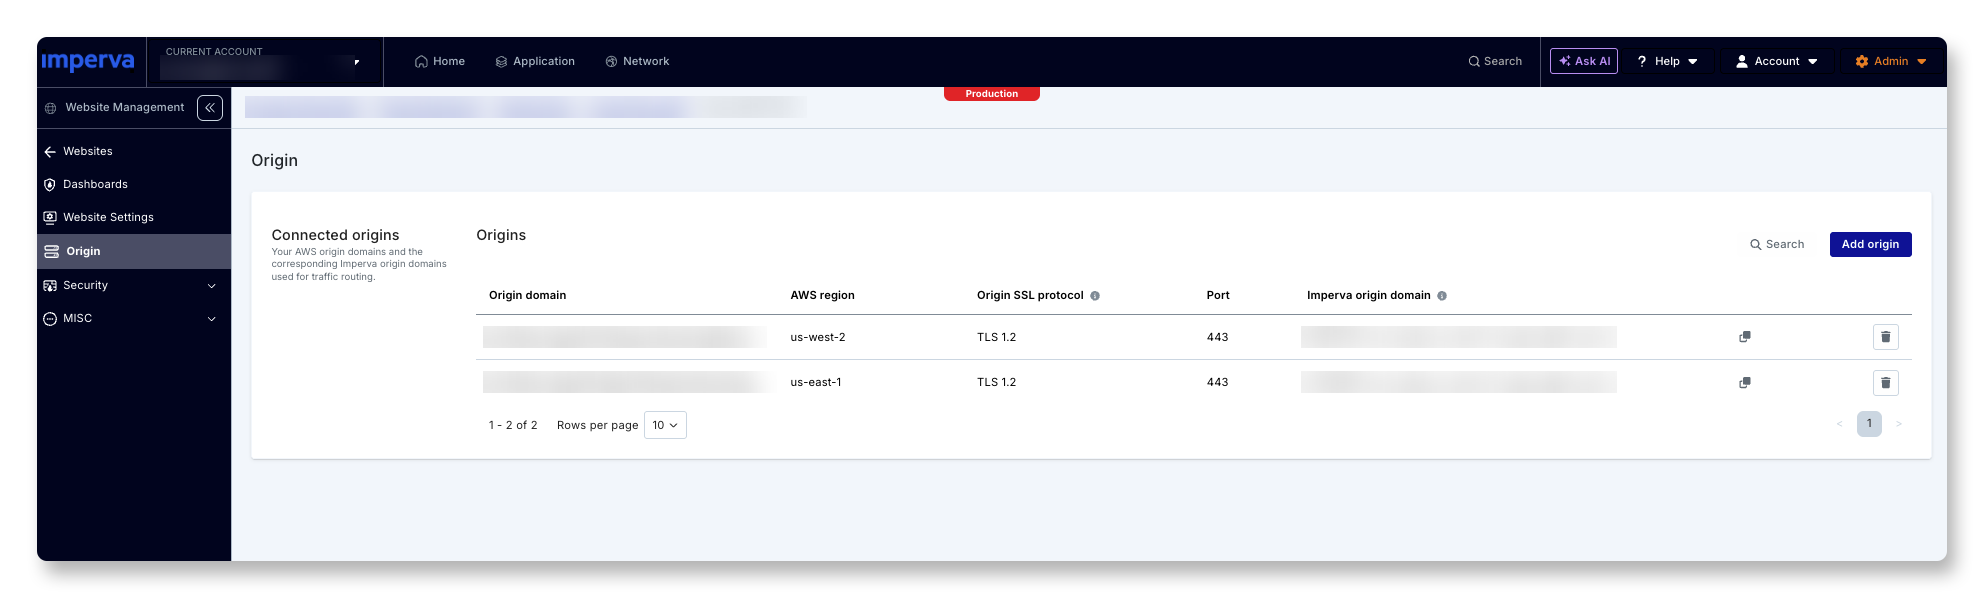
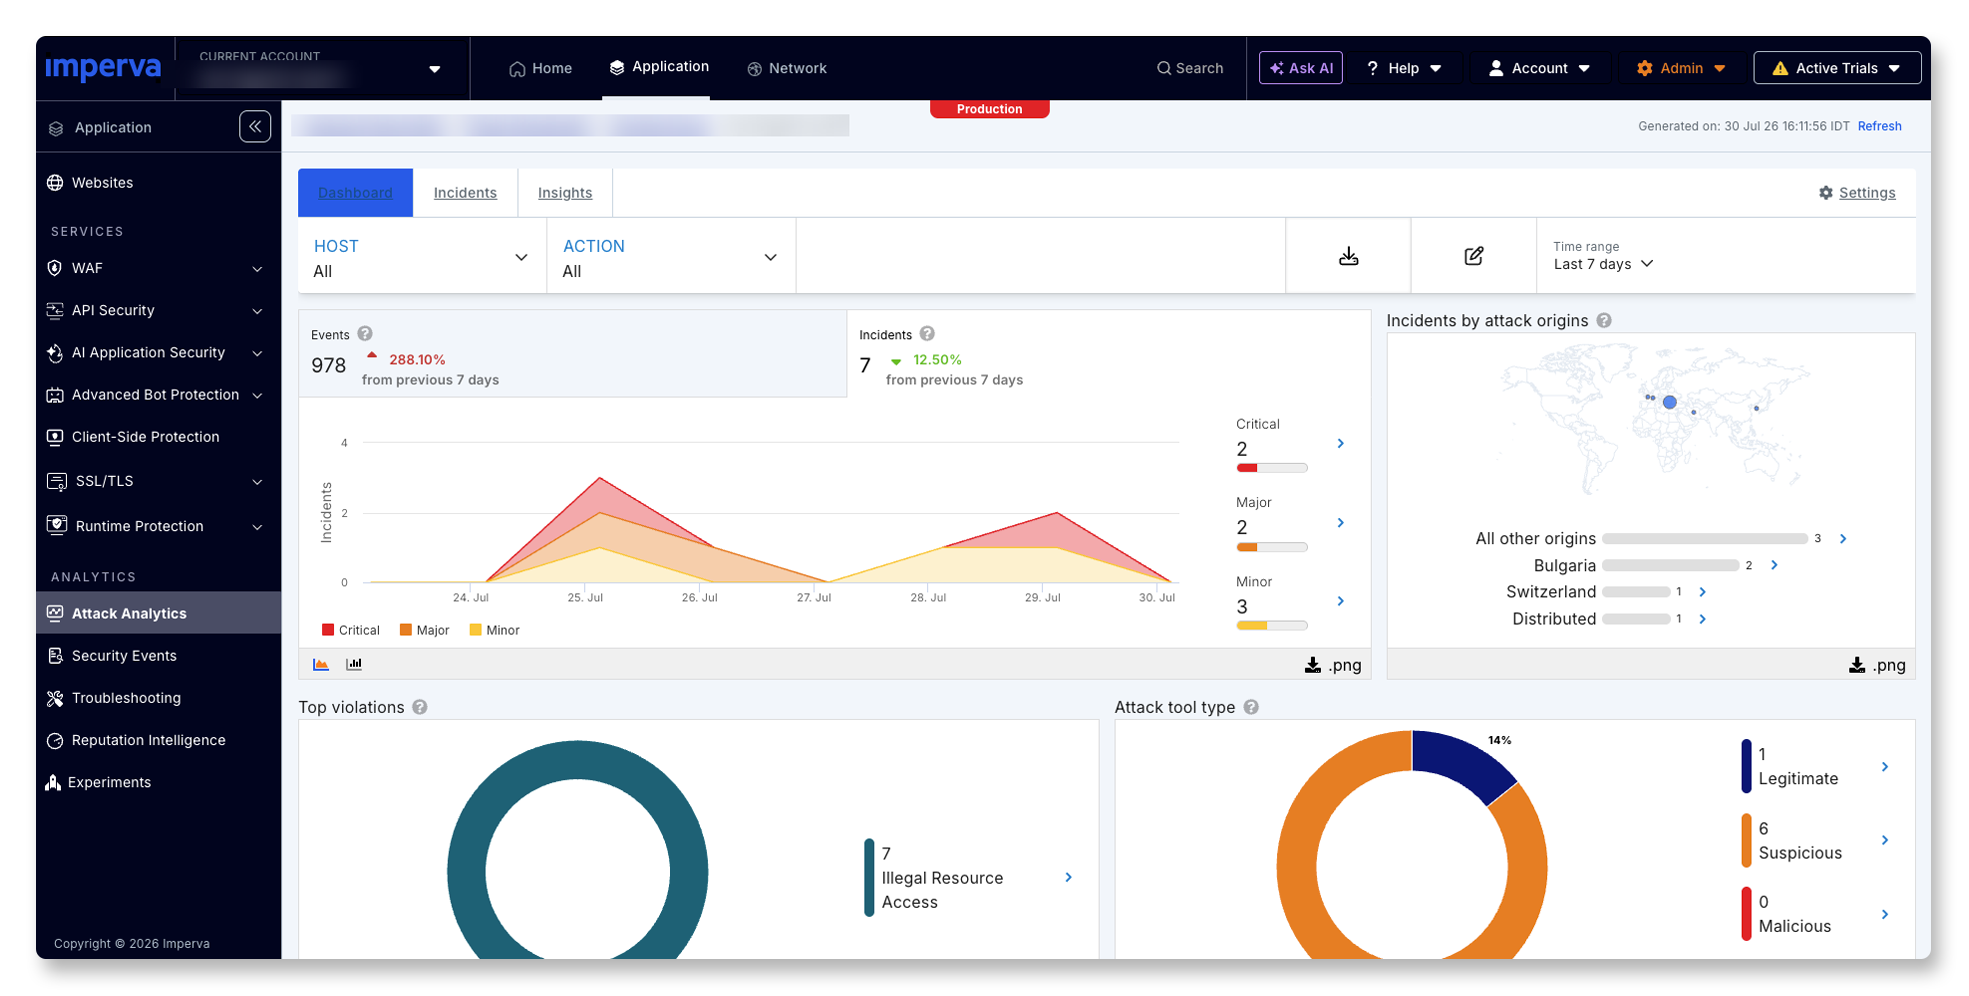
User traffic is routed through Amazon CloudFront, following the same global edge network and delivery path your applications already use. There’s no change to how users access your services—CloudFront continues to handle caching, acceleration, and request routing as normal.
Traffic is inspected in-line within the AWS environment, alongside services like Amazon CloudFront. Requests are analyzed without being redirected to external networks or third-party clouds—keeping traffic local, reducing latency, and aligning with AWS-native architectures.
Imperva applies advanced detection to analyze requests as they pass through the application delivery path, identifying threats such as bots, automated attacks, and API abuse. Malicious traffic is blocked before reaching origin services, without relying on static rules alone.
Allowed traffic continues to your origin infrastructure—such as Application Load Balancer (ALB) or EC2—without disruption. By preserving the CloudFront-based delivery model, performance, scalability, and user experience remain unchanged.
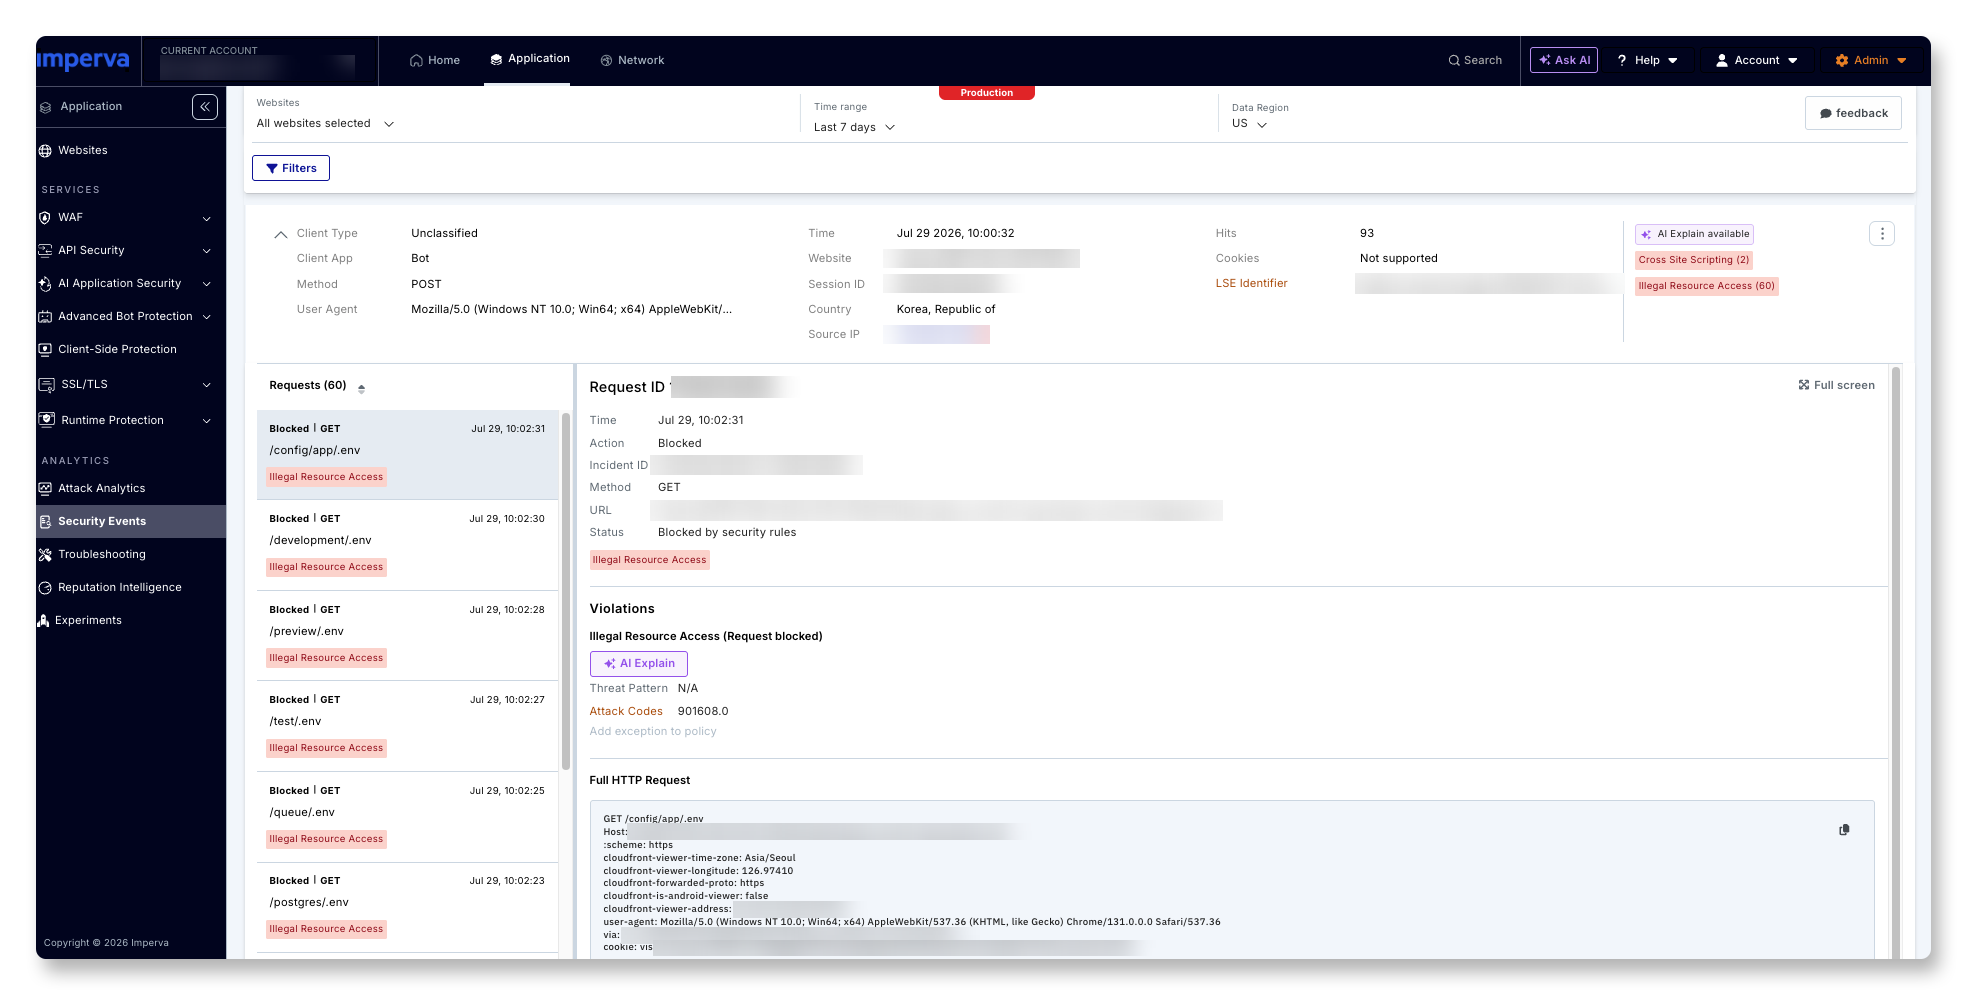
All traffic, threats, and policies are managed through a centralized console, giving security teams a consistent view across AWS-hosted applications. This unified visibility simplifies investigation, accelerates response, and reduces operational overhead at scale.
Imperva for AWS is a fully managed WAAP solution that adds web application firewall, API, and bot protection within AWS. It inspects traffic alongside Amazon CloudFront without requiring architectural changes or external routing.
See for yourself. No strings attached.
Go beyond basic cloud-native protections by adding advanced threat detection, bot mitigation, and API security—without changing how your AWS applications are built or delivered.
Secure high-value web applications and APIs exposed to automated attacks, abuse, and evolving threats—while maintaining the performance and scale provided by Amazon CloudFront.
Add enterprise-grade protection quickly with minimal architectural changes, enabling DevOps teams to keep delivering at speed while security operates in-line with AWS workflows.
AWS WAF provides a strong foundation for protecting applications. Imperva extends this by adding advanced threat detection, bot mitigation, and API security, helping organisations address more complex and evolving threats without changing how applications are delivered in AWS.
No. Traffic is inspected in-line within the AWS environment, alongside services like Amazon CloudFront. This allows organisations to keep traffic within AWS while adding an additional layer of protection.
User traffic continues to flow through Amazon CloudFront as normal. Imperva adds inspection within the delivery path, analyzing requests before they reach origin infrastructure, without introducing external routing or additional network hops.
Imperva combines advanced detection techniques with tuned security policies to accurately identify malicious traffic. This helps reduce unnecessary blocking of legitimate users while maintaining effective protection against real threats.
WAAP (Web Application and API Protection) combines a web application firewall (WAF), API security, bot protection, and DDoS defense in a single managed service. AWS WAF is a configurable, rules-based firewall; Imperva’s WAAP adds automated threat detection, API protection, and advanced bot mitigation on top of your AWS environment.
Yes. Imperva inspects traffic inline within AWS and mitigates bad bots, automated attacks, and application-layer (Layer 7) abuse before requests reach your origin — complementing the network-layer protections you already run in AWS.